Tuesday, February 7, 2012

SQL INJECTION and BLIND SQL INJECTION

SQL Injection is often used to attack the security of a website by inputting SQL statements in a web form to get a badly designed website to perform operations on the database (often to dump the database content to the attacker) other than the usual operations as intended by the designer.(wikipedia). SQL injection is technique that exploits and attack vulnerability from the web application security. Commands, sql statement and query embeded SQL is used to penetration test the vulnerability to injected web form into the database, change data or dump the database.

The following line of code illustrates this vulnerability
statement = "SELECT * FROM users WHERE name = '" + userName + "';"
This SQL code is designed to pull up the records of the specified username from its table of users. However, if the "userName" variable is crafted in a specific way by a malicious user, the SQL statement may do more than the code author intended.
' or '1'='1
Or using comments to even block the rest of the query (there are three types of SQL comments, you can  
SQL injection is used to :
  • Perform operations on the database
  • Bypass authentication mechanisms 
  • Read otherwise unavailable information from the database
  • Write information such as new user accounts to the database
Three forms of SQL injections :
  • Redirection and reshaping a query
  • Error message based
  • Blind injection
BLIND SQL injection
Blind SQL Injection is one of the database exploitation techniques that are different from sql injection in which the normal value will be issued but a blind sql injection techniques will not issue any value but the value that we will find out by trial and error will value the test true or false value, Here we use the command
mid () = almost the same function as substring ()
char () = is a variable of character

To test a bug (vulnerable) :
Sql injection :
By inserting the statements  "and 1=0 dan and 1=1"
www.victim.com/client.php?id=3 and 1=0
www.victim.com/client.php?id=3 and 1=1  
maybe have vuln....

Blind sql injection :
Using query: "and mid (user (), 1,1) = CHAR (65)"
mid (user () 1,1) = in this case we do not know the value, so we try and try of what the value of user "()" we try empty and 1.1 points behind () is that while the sequence of CHAR value is in decimal and variables (65) is the decimal value. in the ASCII table 65 is A.

www.victim.com/client.php?id=3and mid(user(),1,1)=CHAR(65)  if with the statement we have false we must try other statment by change the value until we have the true.


EXPLOIT WEBMIN AND CRACKING PASSWORD USING JOHN THE RIPPER (part 2)

Day 6 


Tools :
  •  JTP (John The Ripper)
Target :
  • Cracking password after exploit /etc/shadow
In the post EXPLOIT WEBMIN USING EXPLOITdb TO HAVING PRIVILEGE ESCALATION (part1) is about how to use exploitdb to exploit victim, the goal from it is list user account (username and password), Now in this sessions i will try to cracking the password from the goal. Read the readme.

Readme JTP
Lets load user account in the directory /home to crack the password

Cracking goalexploitdb
Password unsuccesfully cracked...try againt with other file name.

Cracking againts
Cracking one by one
Unsuccesfully.....Password not cracked .....Why?.....
Because the table of dictionary wordlist in the John The Ripper data not exist....but its post is process and how to cracking password using John the ripper....not all of it can be easy to disassemble

EXPLOIT WEBMIN USING EXPLOITdb TO HAVING PRIVILEGE ESCALATION (part1)

Day 6

Tools :
  • Nmap
  • Nessus
  • Exploitdb
Target : Finding user account from 192.168.0.21

Victim
 
First time, Information gathering by scanning target using Nmap. And we have some information from the victim like list of open port and service enumeration fom victim.

IG Nmap scanner
Next, we use Nessus to scanning the vulnerability from victim

Vulnerability with Nessus
Showing three medium vulnerable from open port, you can see the description of this vulnerable service. 

Description of Vulnerable Service
By known in the phase Information gathering, service enumeration and vulnerability assesment. I choose open port 10000 with vulnerable service webmin.  Lets Go to using exploitdb to exploit victims system, search the exploit from the vulnerable services.

Search exploit
 In this list, i choose and copy webmin arbitrary file disclosure exploit (perl) to directory /home. Lets see in the directory home and than excecute.

Exploit
Exploit /etc/shadow
In this picture above the exploite target is /etc/shadow, why? because in the /etc/shadow store all user account (username and password). You can see list of username and encrypted password and after success exploit it i am copying file /etc/shadow to my /home directory with the name file goalexploitdb. in /home directory I tried to break up several user accounts from goalexploit into a many filename with the name pass, pass1, pass2 and pass3.

goalexploitdb in my /home directory
Its Nice day...Next post is the part of this session..


HOW TO USE NetCat AND CYMOTHOA (BACKDOORING) part2

Day 5


Tools :
  • nc traditional
  • Cymothoa
  • Virtualbox (victim)

Ip Address:
  • Attacker 192.168.56.1 Backtrack 5 R1
  • Victim 192.168.56.101 Ubuntu
Cymothoa is a stealth backdooring tool, that inject backdoor's shellcode into an existing process. The tool uses the ptrace library (available on nearly all * nix), to manipulate processes and infect them. In the part one I learn and try backdooring using nc (NetCat), here I will be learn how to using cymothoa to backdooring victim. Lookin the process using netstat and ps -aux.

/bin/bash
 I will try transfering cymothoa to /bin/bash, I see the PID of /bin/bash, see the list of payloads.

Payloads
 I will transfer cymothoa by using the running service protocol http localhost, PID /bin/bash and port 9999.

Running cymothoa
 Infected....
Ceck the netstat in the victim desktop.

Victim netstat 
Not Good situation. Port in the localhost not found :( , maybe I must try harder againt and try the other way...
Maybe try transferred cymothoa to /bin/bash victim. I did it stupidity test to /bin/bash ... :D

Error /bin/bash
OMG …. Error (lol)...(hummer)..
See next parts to see other running and other infected service system (victim).

BACKDOORING USING NetCat part1

Day 5

Netcat is a computer networking service for reading from and writing network connections using TCP or UDP Netcat is designed to be a dependable “back-end” device that can be used directly or easily driven by other programs and scripts. Netcat is often referred to as a "Swiss-army knife for TCP/IP." Its list of features includes port scanning, transferring files, and port listening, and it can be used as a backdoor. (wikipedia)

Tools :
  • nc traditional
  • Virtualbox (victim)
Ip Address:
  • Attacker 192.168.56.1 Backtrack 5 R1
  • Victim 192.168.56.101 Ubuntu
Im a newbie not expert and my english is not fluently but I always try, in this session I learn and try how to make backdoor with nc. Because my nc isnt traditional I must transfer nc.traditional to victim. By using service protocol apache and http. Copy file nc.traditional to directory /var/www
transfer nc.traditional
Ubuntu (Victim) open browser by type Ip Address from attacker and save this file.
Download nc.traditional
Victim : Go to directory file where the nc.traditional saved, and than running the nc

 
running nc.traditional
 Attacker running nc too, this is already running
attacker listening nc.traditional
by cecking id you can known the nc is succes by see th prosess using netstat, ps -aux or by type the ls.

Attacker intrussion Victim
By ls I know what is the list of directory home in the victim, and next I will transfer cymothoa to the victim

Succes Transfer
 File input as like as file output.

Thursday, February 2, 2012

HOW TO EXPLOIT WINDOWS USING METASPLOIT

Day 4 

Exploitation Windows XP Using Metasploit

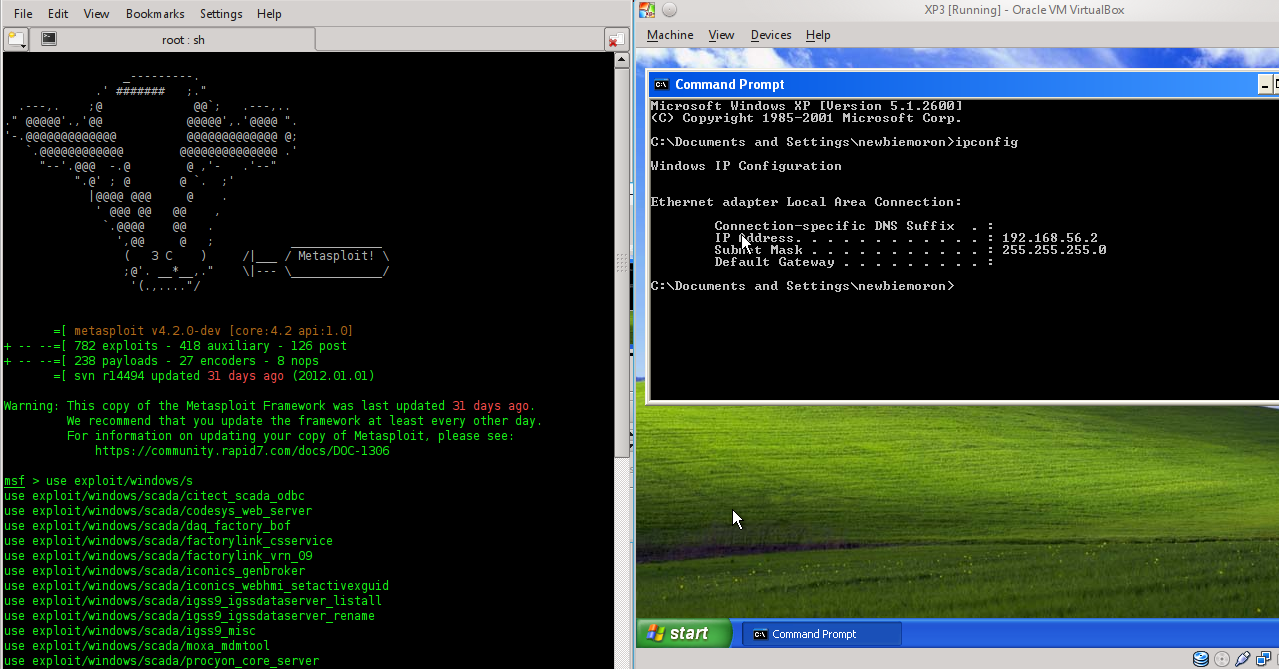
Today learning how to use metasploit to exploit windows xp sp 3 in my virtual lab for penetration testing. In this sessions, step by step from Informations Gathering, Servce Enumeration, Vulnerability Assessment and now we can try to exploit the victim.
First step with known of the vulnerability from target :

Ip Address
 Lets see by nessus vulnerability scanner we can get the vulner from victim :

Vulnerability
Open Port
Services Vulnerability
Can you see the service vulnerabilities, smb and windows server.
All information of vulnerabilities
Port and Vulnerabilities
In the picrture above we known vulnerability from windows xp, two hight risk of vulnerability by port 445 tcp and other port is medium and low risk vulnerabilities.

Ok, with the information of the vulner we can try to exploit with metasploit :
The picture showing ip address client and metasploit, in metasploit by using command like the picture with choosing service from windows. Next we by choossing the exploit and information of services vulnerabilities (smb). you can see  the description of the vuln.


In the picture i choose the smb service with hight risk, and penetration with set ip address oh attacker

Set payload to execute the victim,

The option and and set Ip Address the victim,
In the original you can see the 3 folders in the drive C:\ and i will to make one folder in this drive. Lets to exploit target.

Yaps, exploite successfull
Im in the windows environtman...show list of the folder in the drive..Lets to make a new directory with name newbiemoron (maybe www.newbiemoron.com my expire blog )

Its Funiest Day...Thank You MRP and IS2C


Wednesday, February 1, 2012

How To Install Nessus In Backtrack 5

Days 3
Today, from newbie and a cup of coffe i will be explain how to install Nessus is open source tool for identifying vulnerabilities both configurations error and software bugs, of which the former is more prevalent with network devices.

Open konsole and type this comand :
If the download installation success, next step you must be registration for adding new user. Add user by go to Menu > Vulnerability Assessment > Vulnerability Scanner > Nessus > Nessus Register
 
 
Go home for nessus home page and than you must be agree of the rule agreement for using nessus. After this session you must registration your mail address and go to cek email verivication code from nessus. I you are lucky and success registration lets copy your register code from nesus in the konsole like this.


After enter the registration code and please wait this session. Maybe you can see the process downloading by use bmon (Bandwidth Monitoring) to known the download activities.
 
 
If you are lucky boy you can see this picture, 
Next

 
And you must go to the browser, in this time i am using mozilla. Type localhost:8834 or 127.0.0.1:8834 to starting vulnerability assessment scanner (nessus).
 
 
Nessus is running and already to use....