Friday, February 24, 2012

PRACTICAL SEH : BIG ANT SERVER EXPLOITATION part 1

SEH (Structured Exception Handler) exploit can be written to target a Windows host. We use the buffer overflow vulnerability in the Big Ant Server software as a detailed example of this exploit type.

Purpose Learning :
Understanding the concept of SEH, SafeSEH, Bad Charachter, Payload, Exploit

 
Big Ant Server On Windows
Making the fuzzer with python language to trigger a buffer overflow.
Fuzzer1
Start the BigAnt Server, open the ollydbg and attach process of BigAntServer and play the ollydbg to analisys the process. Next run the fuzzer from Bactrack, after the fuzzer run BigAnt application is normally not the case crash like fuzzing for non SEH.
After Fuzzing
 In the picture above the EIP not overwrite, lets see the SEH chain by view -> SEH Chain.
SEH Chain
This indicates that the application is the SEH. Next cek into the EIP with press SHIFT + F9, the EIP is overwrite with 41414141.
EIP Overwrite
Stack overwite too with charachter AAAAA. Lets cek the stack overflow in the memory dump to see the buffer by right click in the stack overwrite with character AAAA and follow in the dump. In the moemory dump full of 41 41 41 41.
Stack Overflow
Dump
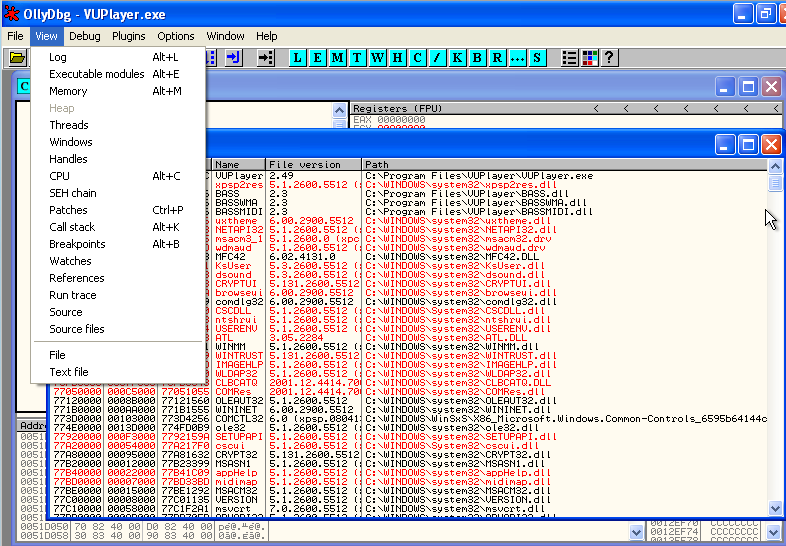
Next lets to see the modules by view the executable modules to know what modules are loaded by the application.
Executable Module
Vbajet module


I choose the vbajet.dll because this file dosnt have the features of image DLLCharacteristics No SEH. To further more analisys the modulle yo can put the module and working with backtrack tools laik MSFPESCAN to accounting and analyze.
MSFPESCAN
Back to the Ollydbg, next phase are find the POP, POP, RETN that are often used. its used to by passing the SEH directly into the EIP and we will be able to controll of the EIP. In the CPU left above by right click and search for sequence of command.
CPU
Find Sequence of commands
POP POP RETN
To be continue

Tuesday, February 21, 2012

FUZZING: DIRECT RETURN VU PLAYER (BASED EXPLOIT)

After trying to exploit the application of RM-Mp3 Converter, try again exploitation "vuplayer". Methods, principles and methods used together with fuzzing and based buffer overflow exploit previously.

VuPlayer On Windows
Tools :
- Victim (VuPlayer, OllyDbg)

After trying to exploit the application of RM-Mp3 Converter, try again exploitation "vuplayer". Methods, principles and how to same with fuzzing and based buffer overflow exploit previously. This time I will not explain more about the process and how to work as before. Read
First time, make the fuzzer with python, ruby, perl or C. I choose the python language.
Fuzzer
Look the fuzzer script, if the fuzzer run it was make a file with the name peterpan.m3u . Peterpan is a one of many kinds famous music group. Ok back to the theme.
Before VuPlayer
After running the fuzzer
Create the pattern
pattern create
Edit the fuzzer and fill the pattern output into the fuzzer
Fuzzer 2
The ESP overwrite...and see the EIP value.
Overflow
Find the where is the byte with pattern_offset
pattern_offset
Edit Fuzzer and then write the DEADBEEF
DeadBeef
Run the fuzzer...and....
EIP Undercontrol
DEADBEEF and NOP (No Operation) stack junk...
Fuzzer Deadbeef and Nop Stack junk
After running the fuzzer....
EIP undercontrol and stack junk with ccccc
Open the Executable modules...
Executable Modules
Choose the module, i choose the SHELL32.dll and open.
Shell32.dll module
Open the SHELL32.dll and searh for JMP ESP so break point ...
Search JMP ESP and Break point
Edit the fuzzer and run againt...
Fuzzer4
After fuzzer run...
Look EIP, stack, and access memory....the value its going to be exploit..Now activated the msfweb (Metasploit)...
msfweb activated
Go to the browser...and open the 127.0.0.1:55555 to open the msfweb. Filter the modules, i am using windows execute command to open the calculator. I choose calculator because the size memory is low.
msfweb filter
Choose the payload...I choose windows execute command to open the calculators...Dont forget to fill the restricted character with 0x00 0x0a 0x0d because its characters make the payloads can't work.
Calculator Payload
Generate the payloads...
Shellcode or payload
Lets fill the payload int fuzzer...
Fuzzer with payload
Run the fuzzer and then lets see the what happens after the fuzzer run the application and try to load a file with a name peterpan.m3u. 


Which occurs vuplayer application not only crash but the application terminate and showing the calculator. The exploit vuplayer application with direct return based buffer overflow succesfully....Its So HOT.

Monday, February 20, 2012

FUZZING: DIRECT RETURN MP3-CONVERTER BUFFER OVERFLOW (BASED EXPLOIT)

REMOTE THE WINDOWS USING EXPLOIT and BUFFER OVER FLOW

This time it tries to do fuzzing to mp3 converter (rm-m3u) that runs on Microsoft Windows XP (victim). Previously been discussed and tested in war-ftp application. Techniques used in buffer overflow is equivalent to the direct return of the previous techniques based exploitation, the difference here will try to make the fuzzer itself does not use a fuzzer that already exist in the exploit-db.

mp3 converter
Rm-mp3 converter on Windows
 Tools :
Victim : Microsoft Windows XP, RM-MP3 Converter, OllyDbg.
Attacker : Bactrack

Ok, we try to make a simple fuzzer. The purpose of making a simple fuzzer without using the exploit-db is to try yourself to understand about fuzzing techniques in a buffer overflow. The following is the result of a simple fuzzer but have not been able to make the overflow on the ESP.
Fuzzer1
Crash
Seen that the fuzzer can not overwrite the ESP. therefore we try to increase fuzzer size. In the sessions i used size 19000. And try to running the fuzzer like this python (fuzzername).py ......Lets see my fuzzer and after fuzzer run. 
ESP OverFlow
Then looking at the bytes where the register is overflow by using pattern_create. by using pattern create  to find out the location of a string in the data packets sent by the fuzzer.
pattern_create
Pattern_create output
 Look, the pattern_create output in the picture above, next we use it and fill into fuzzer. Lets edit the fuzzer like this.
Fuzzer2
So we run again the fuzzer, and look at the rm-mpe converter in the victim. The register ESP overwrite with the pattern and we know the value of EIP. If ESP overwrite and showing the value of EIP. We can find the byte.

EIP number
By using pattern_offset to calculate the byte size of the resulting pattern of olleh pattern_create.
Pattern_offset output
 Lets see the picture above, we know where the byte now, (17417-17425). So after this we edit the fuzzer again like this. By editing a fuzzer in order to conduct experiments to write DEADBEEF the EIP. If it works means that EIP has been undercontroll.
Fuzzer3
After running the fuzzer.
EIP Undercontroll
Next, edit the fuzzer agains with fill the offset value and the nop (no operation) in the fuzzer. Nop is a waste to write ASCII file into the C stack, but will not affect the execution
Fuzzer finall
Running the fuzzer again and lets see in the stack.
Stack with Nop
Next, see the executable modules, usually people choose SHELL32.dll or USER32.dll and i choose the SHELL32.dll to exploited. To open the executable modules with view-executable modules. Double klick and search for JMP ESP.
Executable Modules
Search JMP ESP....
JMP ESP
JMP ESP
Lets change the DEADBEEF in the fuzzer with value from JMP ESP (7C9D30D7). and run the fuzzer.
Fuzzer JMP ESP
The output memory in the stack and memory instruction full with ASCII CCCCC and CC.
Stack and Memory Instructions
After this, breakpoint in the memory instructions by F2 or right click and than break point---> momory on access like this. 
Memory Breakpoint
Open the metasploit to get the payload. Start msf web services : 
Msfweb service running
Lets open the browser. (127.0.0.1:55555), Filter the module and choose the payload. Because i will remote the victim i choose the Bind Shell,.
Find Payload
Fill in the payload
The payload
Ok. we find the payload and than fill the payload into the fuzzer...edit the fuzzer again :) and run it. Lets see the goal. by running telnet in the konsole (attacker Backtrack 5 R1). We are succesfully to remote the victim.
Fuzzer with payload
Telnet
Lets make a directory on the victim's drive.
Make a directory
The directory on the victim
So HOT .... :)